Current state
Status, priority, developing activity, and changes are visible in the context of the work.
[PLATFORM / OVRSYT]
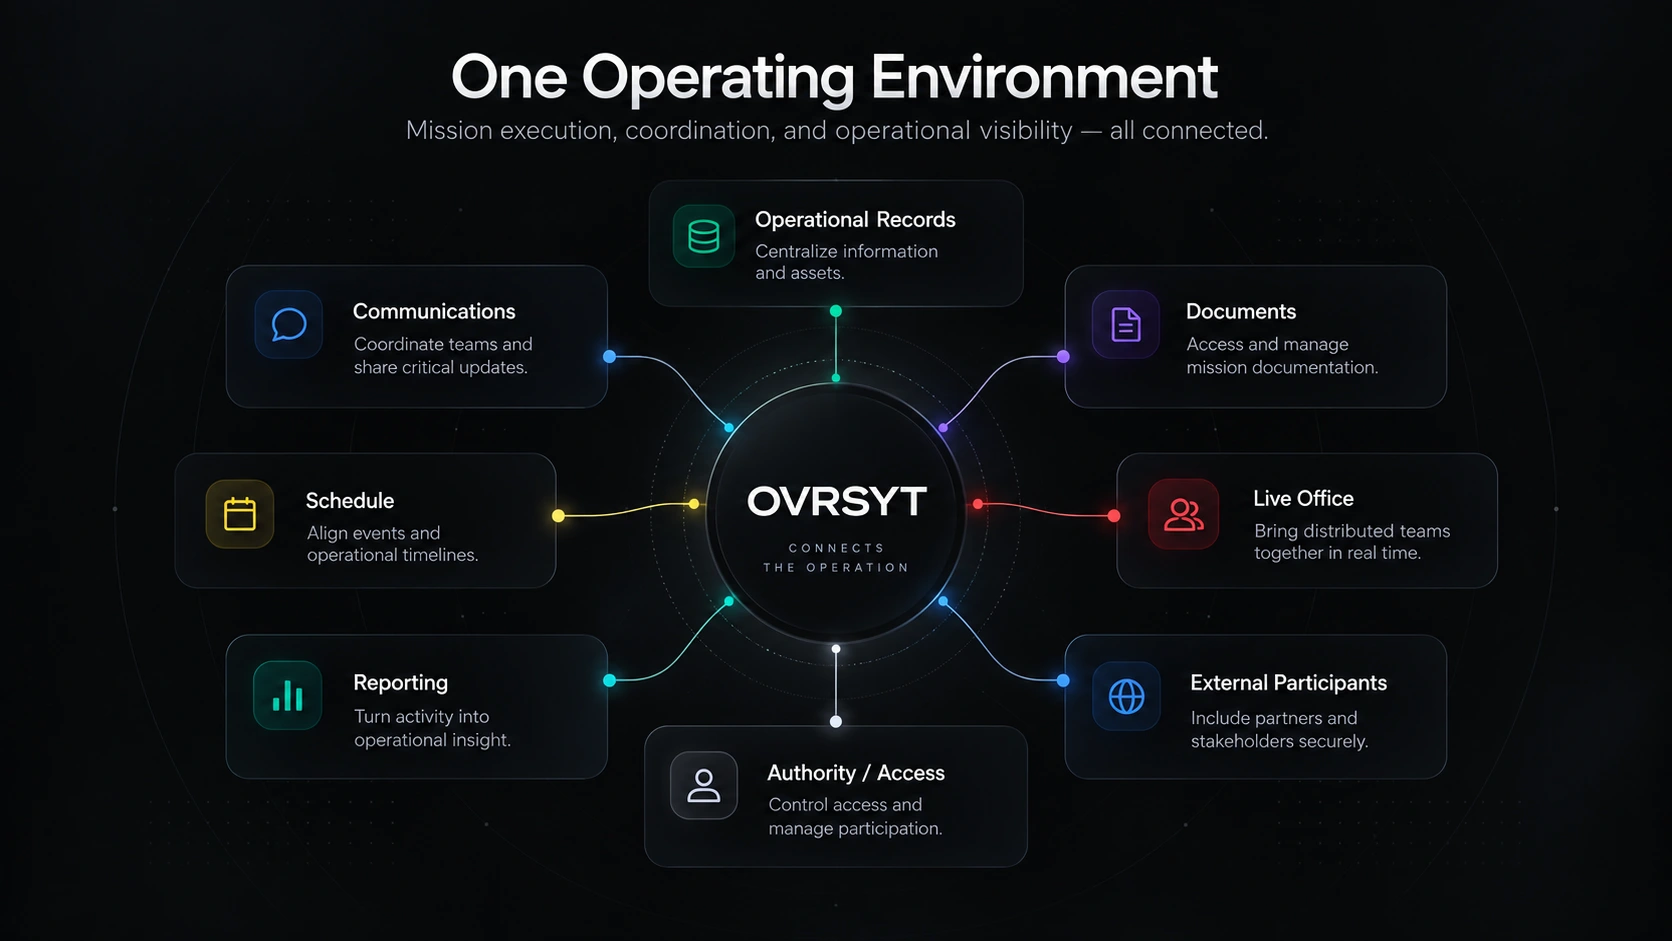
OVRSYT keeps personnel, operational records, schedules, communications, reporting, and execution connected. Each part of the workspace serves the same work, under the same defined authority.
Operating model
An operating environment should not force teams to reconstruct the work each time they change tools. In OVRSYT, each workspace surface draws on a common operating context, with access shaped by the individual, their assignment, and the deployment.
01 / Operational visibility
The operating picture gives personnel a starting point: active work, relevant changes, priorities, and responsibilities. They can move into the detail without first collecting fragments from separate calendars, messages, or files.
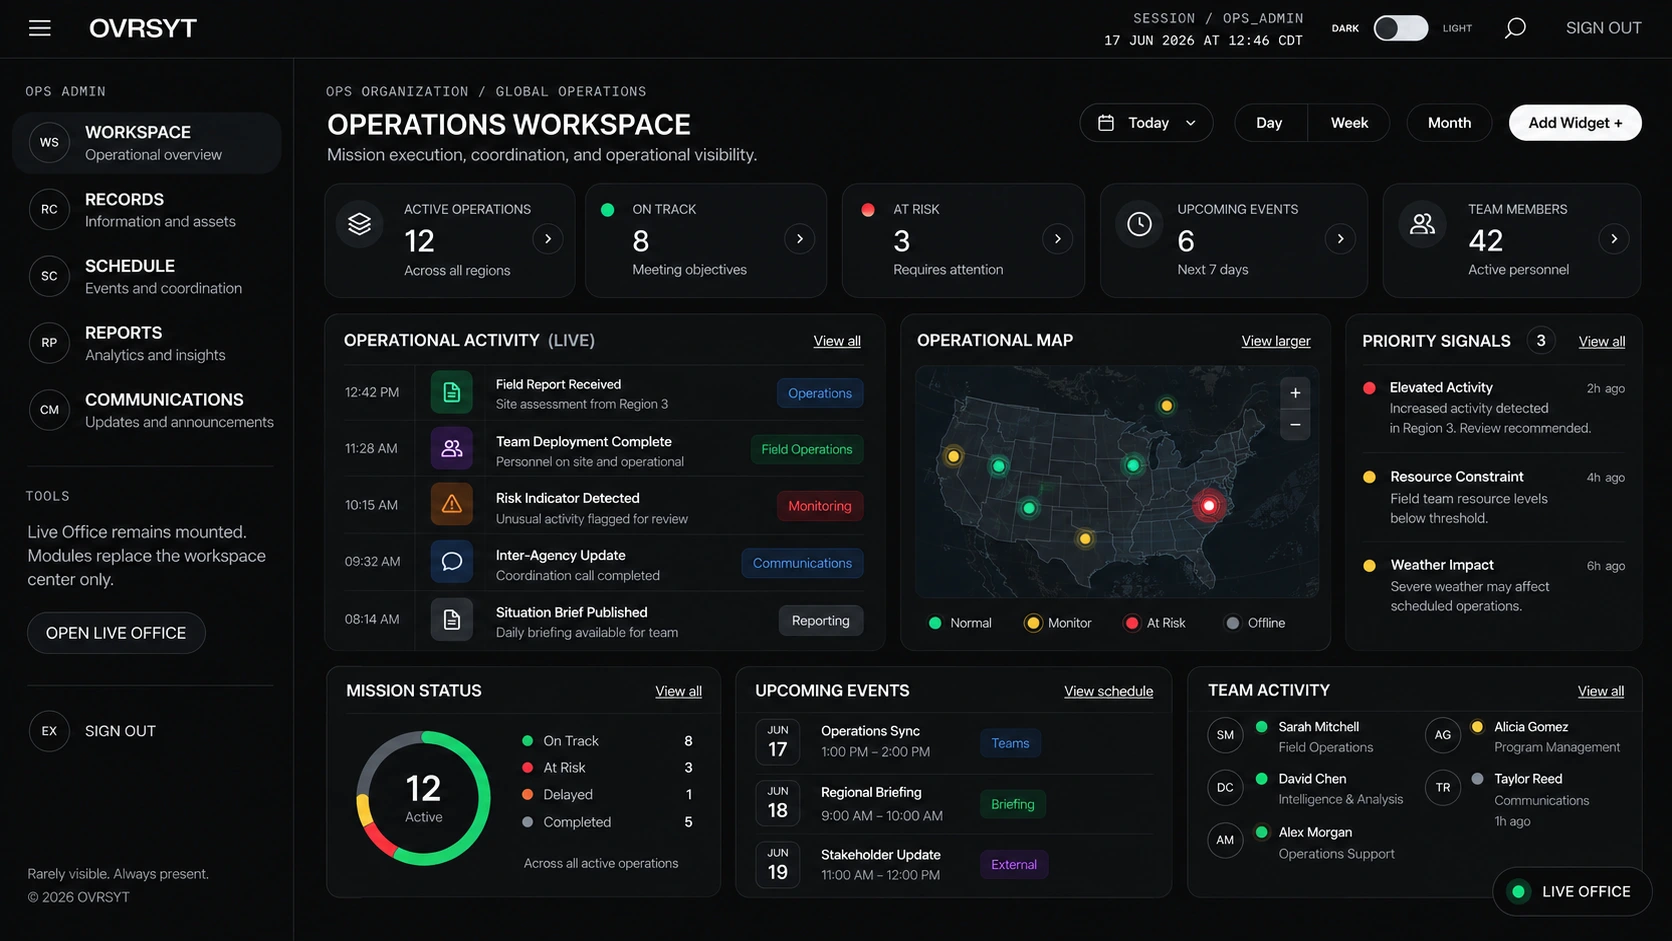
Status, priority, developing activity, and changes are visible in the context of the work.
See assigned personnel and their responsibilities alongside the activity they support.
Follow changes and activity through the workspace rather than reconstructing them from separate messages.
02 / Operational record
The underlying work may be an operation, program, project, inquiry, investigation, or another structured responsibility. The name can change. The requirement does not: preserve the information, personnel, actions, and history needed to understand what happened and what follows.
Keep the central record of work, its participants, status, and supporting information in one place.
The information a person can see and the actions they can take follow their defined role and permissions.
Retain the relevant activity and changes alongside the record they concern, subject to configured workflows.
Documents, schedules, messages, and reports can remain available to the next authorized participant.
03 / Coordination
A schedule sets the pace. Communication aligns the people. The workspace keeps both close to the records and responsibilities they support.
KADENCE connects events, deadlines, availability, and assignments to the work that requires them.
Participants can stay in a live session while independently navigating the records, documents, and schedules their access allows.
04 / Controlled movement
Information can pass between people, teams, and systems without making every recipient an unrestricted participant. Identity, scope, and configured release controls govern that movement.
Identity and assigned permissions determine which actions and information are available.
Access is defined within the relevant workspace, record, and deployment boundaries.
Blackline provides deliberate paths for releasing and controlling access to sensitive material.
Relay supports communication within the broader operating environment.
Command-1 / Service architecture
Command-1 supplies the underlying service architecture for identity, authorization, deployment context, and modular capabilities. OVRSYT brings those services together as an operating environment.
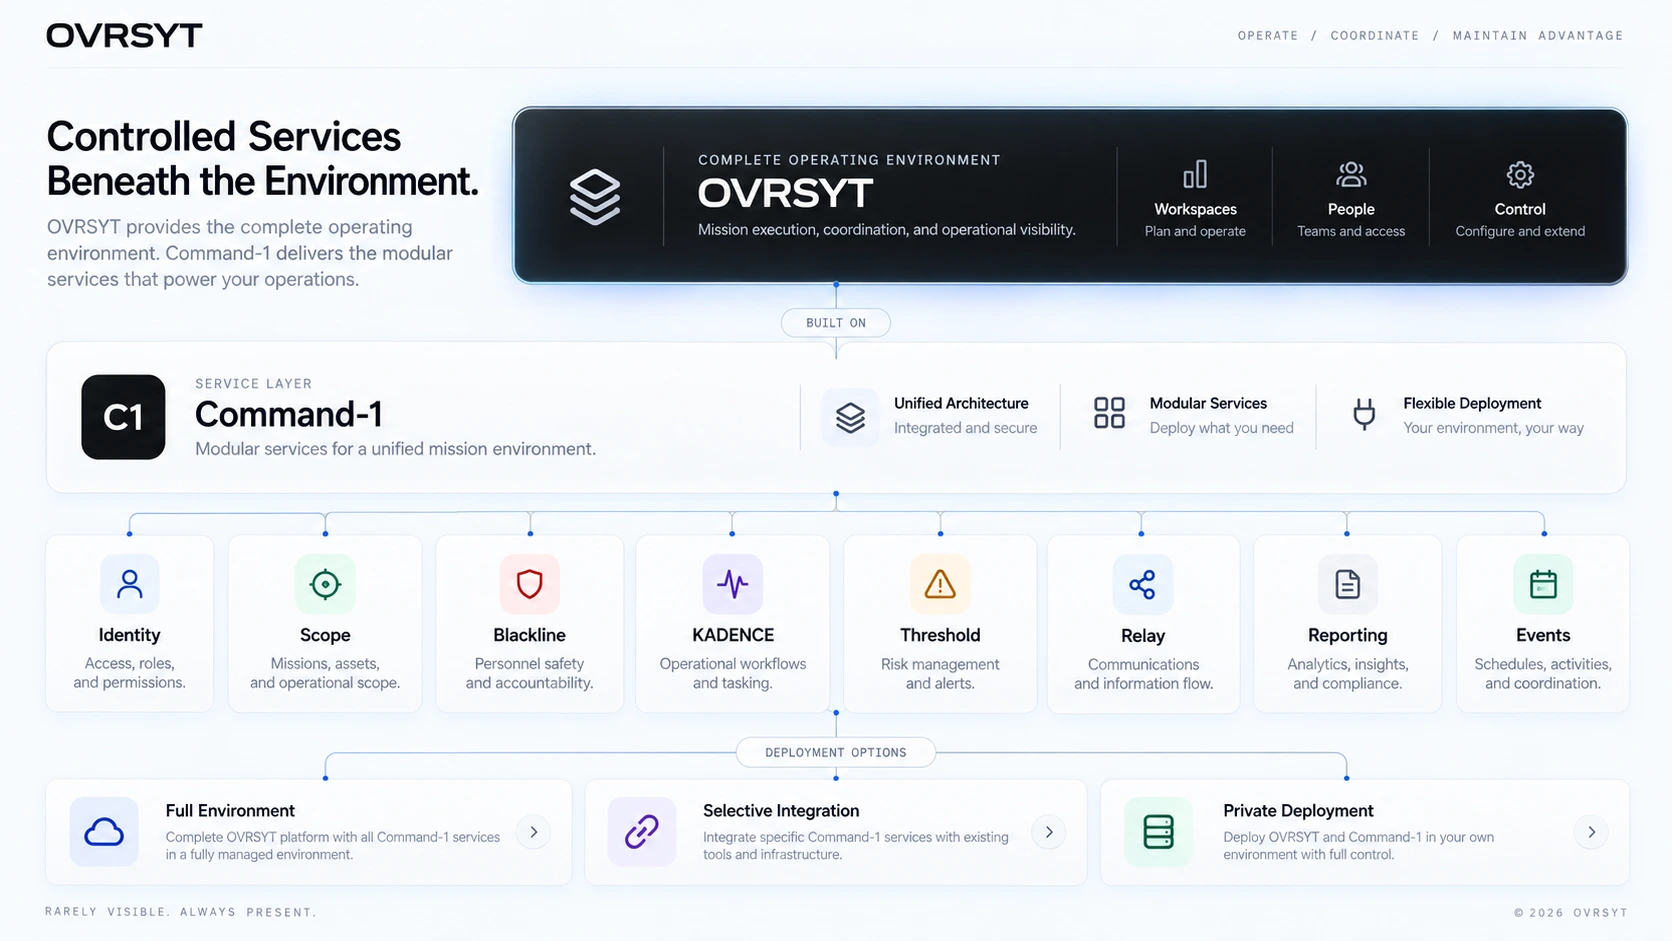
An organization may need the complete OVRSYT workspace, or only selected Command-1 capabilities within an existing system. The requirement determines the integration, not the other way around.
Deployment
Infrastructure, data boundaries, identity, and existing systems shape the deployment. OVRSYT is designed to accommodate those decisions rather than assume every organization operates under the same conditions.
Bring the connected operating surfaces together for personnel, records, scheduling, communications, and reporting.
Use selected Command-1 services where the existing architecture should remain in place.
Configure the operating environment around the organization’s infrastructure, data, identity, and access requirements.
Engage
Begin with the full OVRSYT environment or a specific capability. Aerellus starts with the operational requirement, the authority model, and the systems already in place.
Contact Aerellus